Vibe codingSecurityGovernance
"I didn't write one line of code" is a confession now
A builder bragged he wrote no code and Moltbook went viral. Days later it was a security story, and that line should mean something different to anyone who approves apps at work.
If you approve apps at work, how often does a link land with a proud little caption attached, something like "I didn't write one line of code"? It usually sits under something genuinely impressive and reliably collects the likes and quote posts. Since Moltbook, honestly, I can't read it without wincing a little.
Moltbook was a Reddit-style site for AI agents, which is to say a social network where the bots were the users. Its creator, Matt Schlicht, said in a post on X that he "didn't write one line of code" for the site, and Reuters noted he has championed vibe coding before, so this wasn't a slip so much as the actual pitch. And the pitch worked, at least for a while. CIO.com wrote that "the hype machine was revved up to the max," with the trend spreading thanks to "leading AI profiles," and the posts that travelled furthest were the eerie ones (Reuters described viral posts on X suggesting the bots were looking for private ways to communicate).
Only later did anyone look closely at the numbers. Moltbook claimed 1.5 million agents, but Wiz's researchers found 17,000 human owners behind them, which works out to 88 agents for every person. The researchers CIO.com cited put the probability that the bots came up with the most startling stuff themselves as "quite low," and the possibility of human control of the content as "quite high," while Reuters said it could not independently corroborate whether the posts were actually made by bots. So a good chunk of the buzz was people doing what people on social media do, and since I work in marketing, I'm in no position to throw stones.
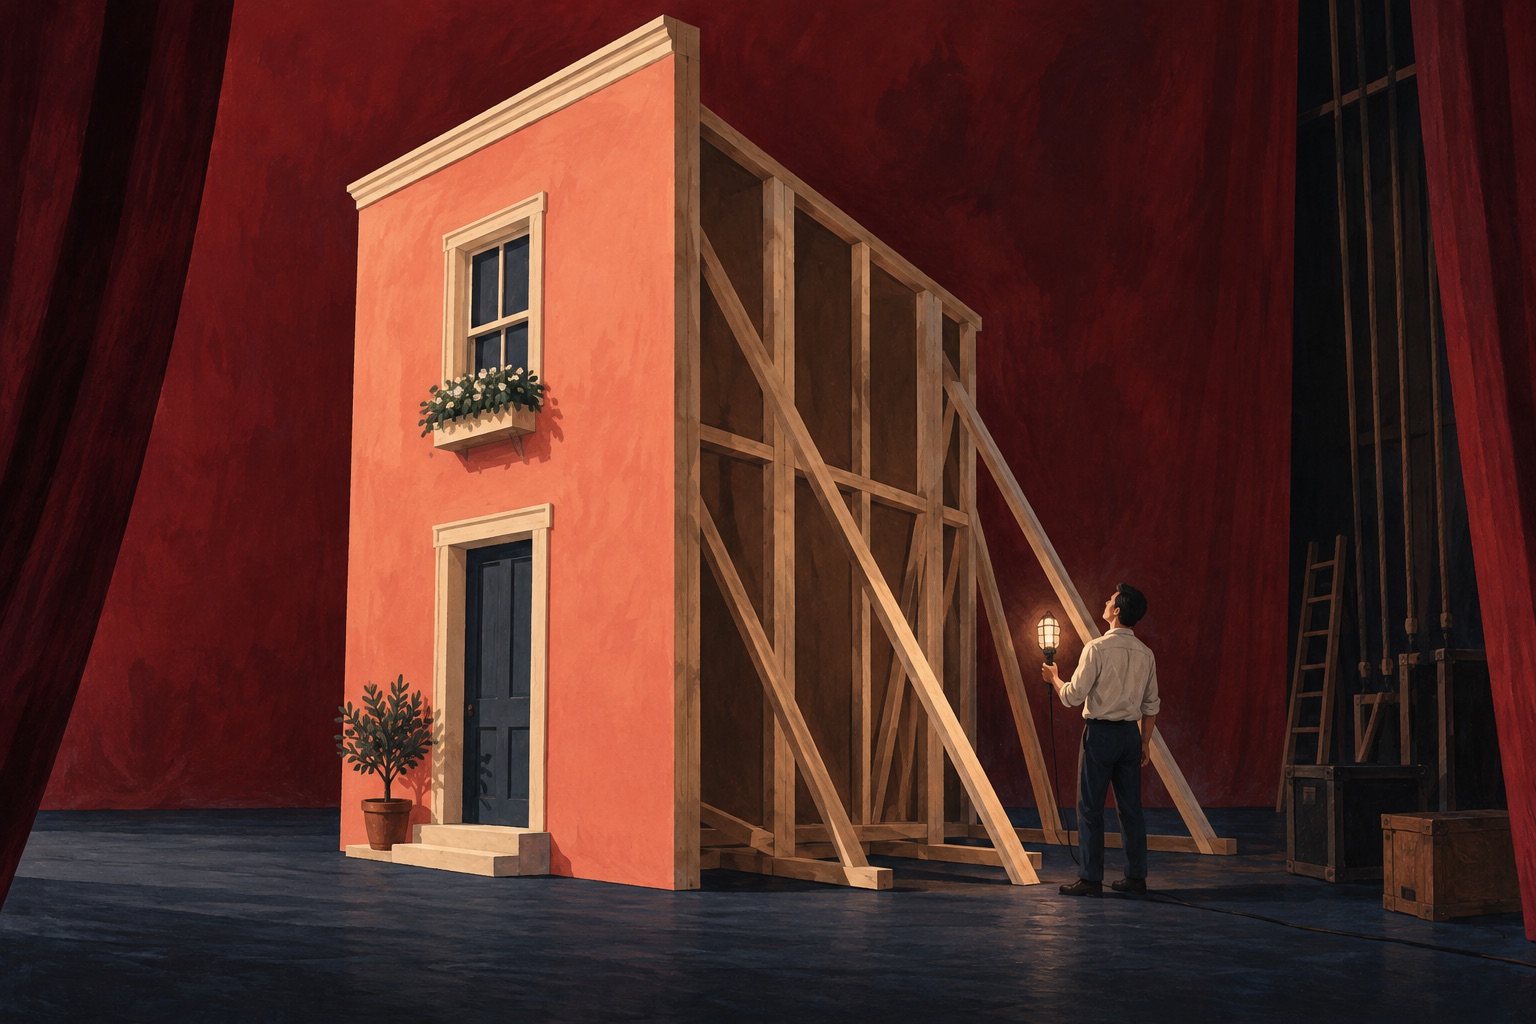
What was behind the curtain
The follow-up travelled a lot less far than the launch, which is usually how it goes. Wiz found a Supabase API key exposed in Moltbook's client-side JavaScript (the code your browser downloads when you open the page). That can actually be fine as long as the database has Row Level Security, meaning rules about which rows each user is allowed to read and change. On Moltbook, though, Wiz wrote that "this critical line of defense was missing," and "without RLS policies, this key grants full database access to anyone who has it."
Sitting in there were 1.5 million API authentication tokens, 35,000 email addresses and 4,060 private conversations between agents, some of which contained plaintext OpenAI API keys. Even after the first fix blocked reading the sensitive tables, write access to public tables stayed open, and Wiz's team was able to modify existing posts on the site.
To be fair to the builder, the response was quick once the problem had been raised. Wiz's disclosure timeline has first contact by X DM at 21:48 UTC on 31 January and the final fix, securing all tables, at 01:00 on 1 February, so four fixes in a little over three hours. That doesn't look like someone who didn't care. I could be wrong here, but it reads more like someone who hadn't been asked the question until a stranger asked it.
Wiz cofounder Ami Luttwak told Reuters it was "a classic byproduct of vibe coding," and that "many times people forget the basics of security." Wiz's own write-up calls it "a recurring pattern we've observed in vibe-coded applications," which suggests this is less about one unlucky builder and more about a habit that comes with the way these apps get made.
CIO.com put it more bluntly than I would, warning against the urge to "throw all security considerations in the trash" just because something seems fun. It also called the mix "part curiosity, part FOMO, and part hype" a "security cocktail that is too hard to resist," which describes the people sharing the thing as much as its builder, because nobody stops to check the locks on something that's making them laugh. Australian security specialist Jamieson O'Reilly, quoted by Reuters, said the site's popularity "exploded before anyone thought to check whether the database was properly secured." The attention arrived first and the questions showed up afterwards, and I suspect that order plays out far more often than the cases that end up in a security firm's blog.
What the sentence should mean at work
To be clear, none of this makes vibe coding bad. Building by prompting is real, the people doing it are making useful things quickly, and honestly I'd rather more people could do it.
I do think the meaning of that sentence has flipped, though. On X, "I didn't write one line of code" means "look how quickly I made this." Read by someone in security or IT, it should mean something more practical, which is that maybe nobody has gone through who can read and write what. So go through it, not as a reason to block the app or to sneer at whoever made it, but as a reason to look at access before the link gets shared. Check who can read the data, who can change it, and whether anything sensitive is sitting in the code the browser downloads, the way you'd read a contract before signing it however friendly the person handing it over happens to be.
Wiz has the line I'd want every team to remember: "the barrier to building securely has not yet caught up." Building got easy and building safely hasn't, at least not yet, so until it does the review is going to have to do the catching up. That's the unglamorous part we care about at Workbricks, having access rules in place before an app reaches anyone, and it isn't very shareable, which is probably why it gets skipped so often.